
Fintech companies occupy an uncomfortable position in the regulatory landscape. They are expected to innovate fast and deliver frictionless digital experiences, while simultaneously meeting the same Know Your Customer and Anti-Money Laundering obligations that govern traditional banks with decades of compliance infrastructure behind them. For a startup processing its first thousands of accounts, or a scale-up entering new markets, these obligations are not optional. Regulators treat fintech platforms as fully accountable for the identity and risk profile of every customer they onboard, regardless of how recently the company was founded.
The practical solution to this tension is purpose-built identity verification for Fintech, a category of technology designed to meet the specific document reading, biometric matching, and risk assessment requirements of financial regulation while integrating natively into the digital-first products that fintech companies build. When implemented correctly, it transforms compliance from a bottleneck into a scalable automated process.
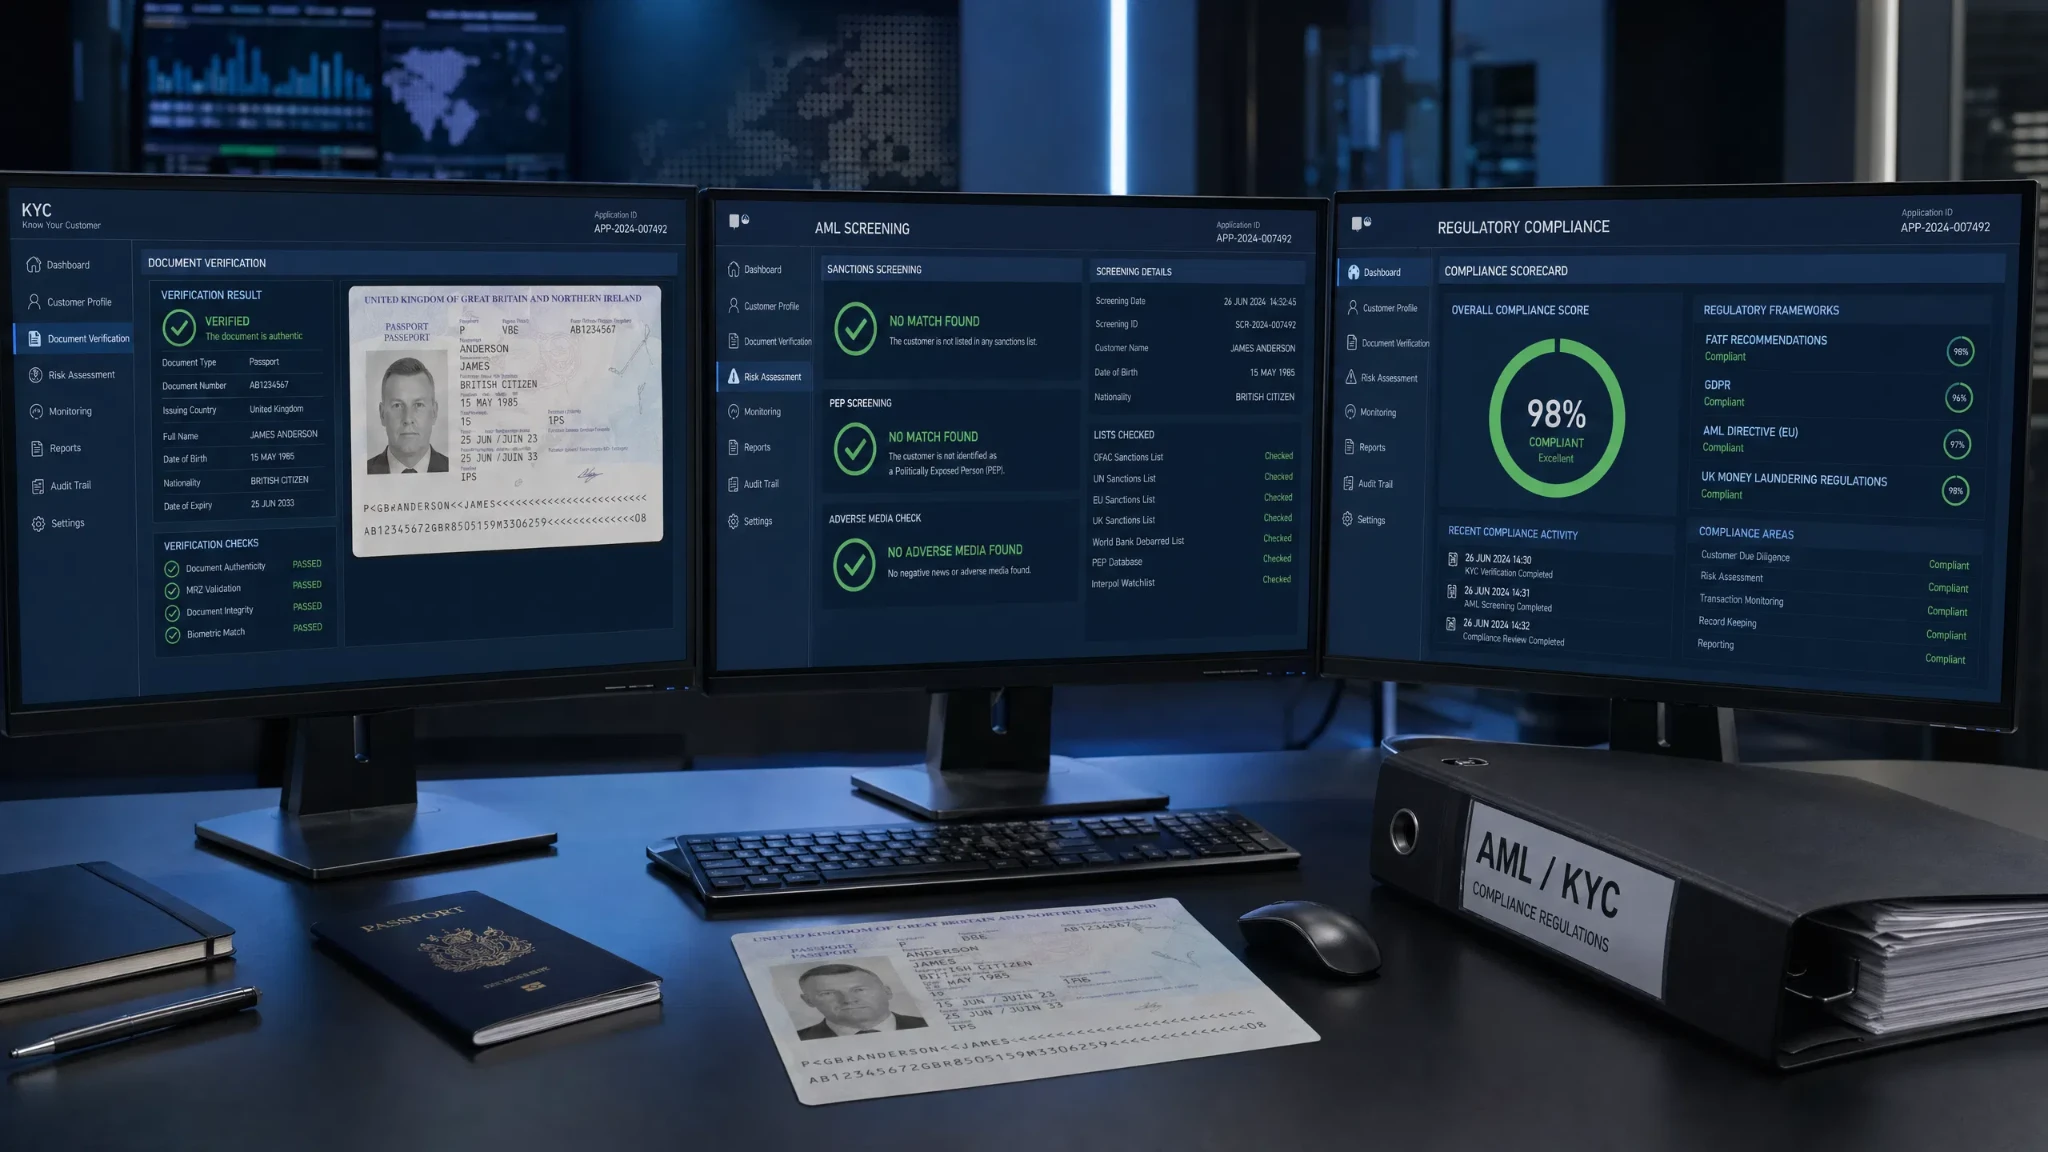
What KYC and AML Compliance Requires from Identity Verification
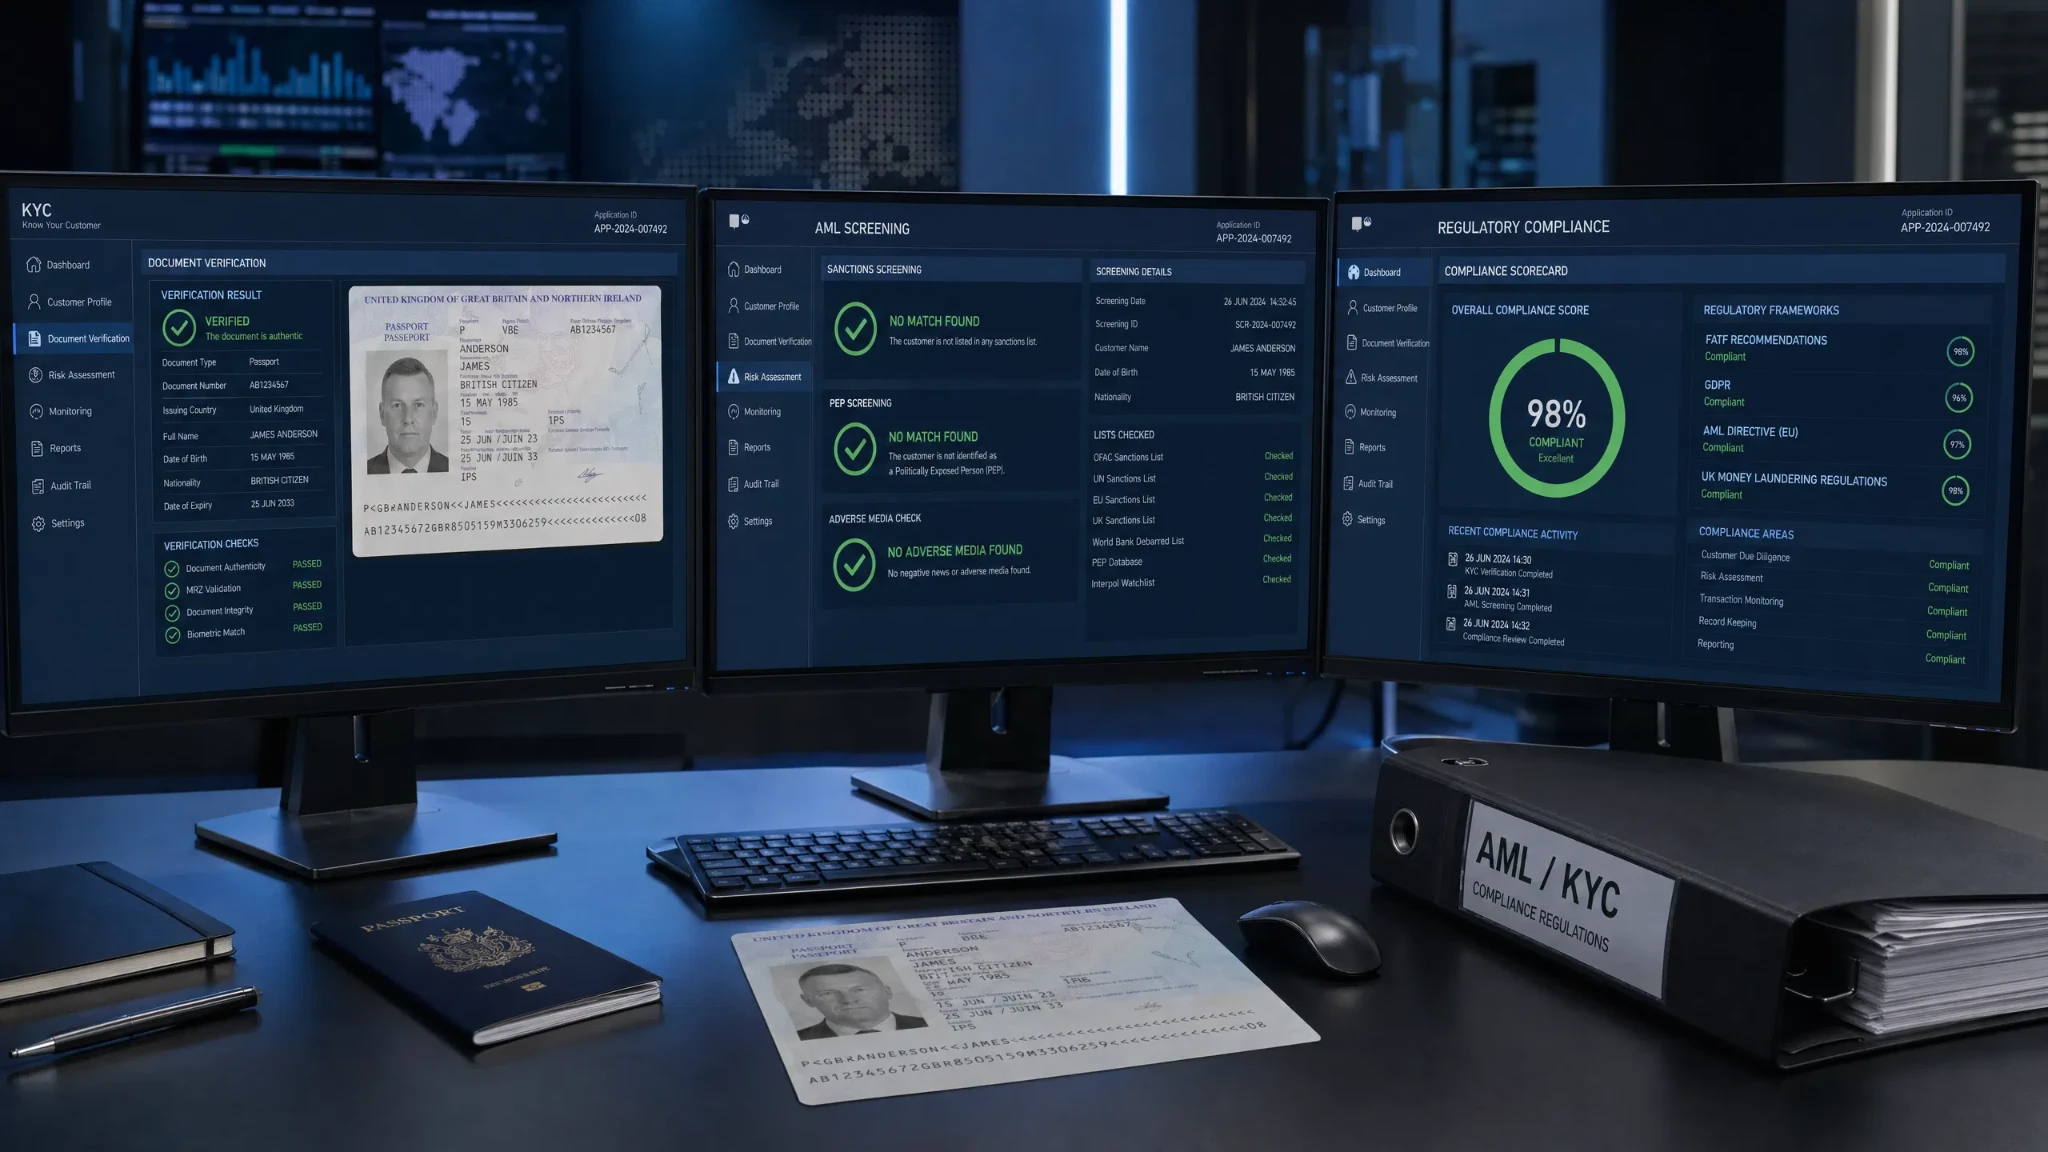
KYC, or Know Your Customer, is the regulatory requirement for financial institutions to verify the identity of their customers before providing services, and to maintain records of that verification for audit purposes. AML, or Anti-Money Laundering, is the broader framework of regulations requiring financial institutions to detect, prevent, and report transactions that may involve the proceeds of criminal activity. In other words, KYC answers the question of who the customer is, while AML answers the question of whether their financial behavior is consistent with legitimate activity.
Identity verification sits at the foundation of both frameworks. A financial institution that cannot reliably confirm who its customers are cannot perform meaningful AML screening, because the screening depends on having accurate customer identity data to match against sanctions lists, politically exposed persons (PEP) databases, and adverse media sources. That’s why KYC and AML are structurally interdependent, and why failures in identity verification tend to create cascading compliance failures across both.
At a minimum, KYC-compliant identity verification requires the following elements.
- Identity document collection and verification: obtaining a government-issued identity document from the customer and confirming that it is genuine, valid, and belongs to the person presenting it.
- Personal data extraction and record creation: reading the customer’s name, date of birth, nationality, and document number, and storing this information in a structured, auditable customer record.
- Sanctions and PEP screening: checking the verified customer identity against official sanctions lists and PEP databases to identify prohibited or elevated-risk individuals.
- Ongoing monitoring: maintaining the accuracy of customer records over time and re-verifying identity when risk indicators change or periodic re-KYC requirements are triggered.
Where Fintech Companies Most Commonly Fall Short on Identity Verification
Regulatory examinations of fintech platforms reveal a consistent set of compliance gaps. Understanding these failure patterns helps product and compliance teams prioritize where to focus verification investment.
Inadequate Document Authenticity Checks
A majority of early-stage fintech products implement identity verification by collecting a document image and extracting the visible data fields, without performing structural validation of the document itself. This approach confirms that a document image was submitted but does not verify that the document is genuine. A forged passport that displays accurate-looking fields will pass this check, while a real passport with minor physical damage may fail it if the system lacks the sophistication to distinguish between the two.
Missing or Weak Liveness Detection
KYC regulators in a growing number of jurisdictions require biometric confirmation that the person submitting the document is physically present during verification. Collecting a selfie without liveness detection, which is the step that confirms a live person is present rather than a photograph or screen replay, does not satisfy this requirement. A self-submitted photo against a stolen document image passes a simple selfie check but fails a liveness-plus-biometric-match check.
Incomplete Audit Trails
Regulatory examiners reviewing a fintech company’s KYC records expect to find a complete, timestamped record of every verification decision, including the document type reviewed, the data extracted, the checks performed, the outcome, and the basis for any manual override. Platforms that log only the final pass or fail outcome, without the supporting detail, cannot demonstrate the quality of their verification process to a regulator and are vulnerable to findings of inadequate due diligence.
Static Rules in Dynamic Risk Environments
KYC and AML requirements evolve continuously as regulators update guidance, add new sanctions targets, and respond to emerging fraud patterns. Fintech platforms that build verification rules directly into application code, rather than using configurable compliance infrastructure, face recurring engineering cycles to keep pace with regulatory changes. Given this operational constraint, many platforms fall behind current requirements without realizing it until an examination reveals the gap.
Where Identity Verification Has the Highest Compliance Impact in Fintech
Compliance risk is not uniformly distributed across the customer lifecycle. The following touchpoints represent the highest-stakes verification moments for fintech platforms.
Account Opening and Initial KYC
The initial onboarding verification is the foundation of the entire compliance relationship with a customer. Errors at this stage, such as accepting a forged document or failing to screen against a sanctions list, create a compliance liability that can persist for the lifetime of the account. Here is when investment in high-accuracy document verification and complete screening integration is most clearly justified.
High-Risk Product Access and Limit Escalation
Regulations frequently require enhanced due diligence for customers accessing higher-risk products, such as investment accounts, crypto wallets, or high-value credit facilities, or when a customer’s transaction volume or balance crosses a defined threshold. Identity verification at these escalation points ensures that the enhanced scrutiny required by regulation is actually applied, rather than assumed to have been covered by the initial onboarding check.
Cross-Border Services and Market Expansion
Each jurisdiction where a fintech company operates may impose different identity verification requirements, specifying acceptable document types, mandatory biometric steps, or data localization rules. Apart from the core verification capability, platforms expanding internationally need configurable compliance rules that can be applied on a per-market basis without requiring separate engineering implementations for each country.
Periodic Re-KYC and Trigger-Based Re-Verification
Customer relationships must be maintained as well as established. Regulators expect that customer records are refreshed when risk indicators change, such as a change in the customer’s country of residence, a significant increase in transaction activity, or a new adverse media flag. Automated trigger-based re-verification workflows allow fintech platforms to fulfill this requirement at scale without manual case management for every refresh event.
What Reliable Identity Verification for Fintech Should Have
Fintech compliance teams evaluating verification platforms need to assess capabilities across accuracy, regulatory coverage, and operational dimensions. The following criteria define a solution adequate for regulated financial services.
- Document verification with authenticity analysis, not just OCR. The platform should check MRZ integrity, document number format, security feature indicators, and internal data consistency. We recommend requesting a detailed description of the authenticity checks performed, not only an accuracy headline figure.
- Integrated liveness detection and biometric matching. Both components should be present as standard features, not optional add-ons, and the liveness method should be documented as meeting the requirements of the relevant regulatory jurisdiction.
- Sanctions and PEP screening as part of the verification workflow. Identity verification and sanctions screening should be connected in a single workflow so that a verified identity triggers screening automatically. Separate processes create operational gaps where screening may be omitted or delayed.
- Configurable jurisdiction rules with admin-level management. Compliance rules should be adjustable through an administrative interface without requiring code changes. You should attentively analyze the vendor’s process for incorporating regulatory updates, including the typical lag between a regulatory change and its availability in the platform.
- Complete, structured audit logs with decision detail. Every verification event should generate a log that includes the document type, extracted fields, check results, screening outcomes, and the identity of the operator or system that made the decision. These records must be exportable in formats suitable for regulatory examination.
- Data residency and processing options. Some jurisdictions require that customer identity data be processed and stored within their borders. Pay attention to the vendor’s data residency options and whether on-premise or private cloud deployment is available for markets where this is required.
How to Build a KYC and AML-Compliant Verification Infrastructure
Building verification infrastructure that genuinely satisfies regulatory requirements requires coordination between product, engineering, and compliance functions. The following steps outline the key implementation priorities.
- Map the regulatory requirements for each current and planned market before selecting a platform. KYC and AML rules differ significantly across jurisdictions. It will be helpful to produce a requirement matrix that specifies acceptable document types, biometric requirements, screening obligations, and data retention rules for each market, before evaluating vendor capabilities against it.
- Treat the audit log as a compliance deliverable, not a technical byproduct. Define the content, format, and retention period for verification records at the design stage. The audit log is what a regulator will review, so its structure should be designed with that audience in mind, not optimized for technical convenience.
- Connect verification to AML screening in a single automated workflow. Manual handoffs between verification and screening create opportunities for cases to fall through. The verification outcome should automatically trigger screening, and both results should be logged in the same customer record.
- Build a risk-tiered verification model. Not every customer needs the same level of verification. We recommend implementing a tiered model in which initial onboarding meets a standard KYC threshold, and higher-risk customers or higher-risk transactions trigger enhanced verification steps automatically based on configurable risk rules.
- Establish a regulatory change management process. Assign clear ownership for monitoring regulatory developments in each market, define a process for translating regulatory changes into platform configuration updates, and set a maximum acceptable lag between a regulatory change and its implementation in the verification workflow.
Conclusion
Identity verification for fintech is not simply a technology implementation. It is a compliance infrastructure that must be designed to satisfy specific regulatory requirements, generate defensible audit records, and adapt to evolving rules without repeated re-engineering. The most common failures, inadequate document authenticity checks, missing liveness detection, incomplete audit trails, and static compliance rules, are all addressable with the right platform and the right implementation approach.
Fintech companies that build this infrastructure correctly gain a competitive advantage as well as a compliance posture. Faster onboarding, lower fraud losses, and a clean regulatory record all contribute to sustainable growth. First of all, it is crucial to select a verification platform that genuinely meets regulatory standards. Secondly, the operational processes surrounding that platform need to be designed with the same rigor applied to the technology itself.